Everything a service provider runs on, in a single pane of glass.
Purpose-built workflows and guidance for the industries you serve.
Guides, proof and documentation to get more from ITarian.
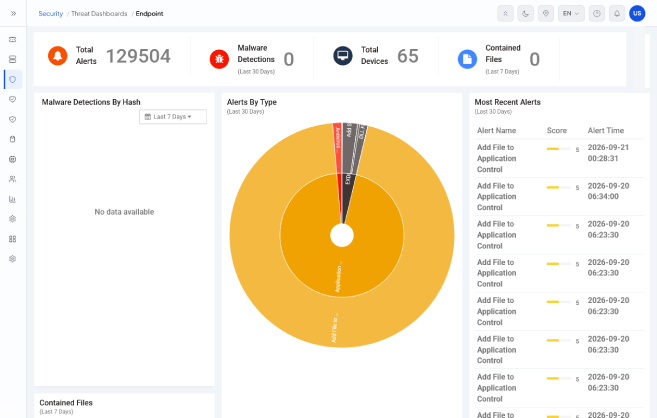
Protect customer endpoints against known and unknown threats with prevention-first security, automated containment and centralized control.

Everything you need to protect endpoints
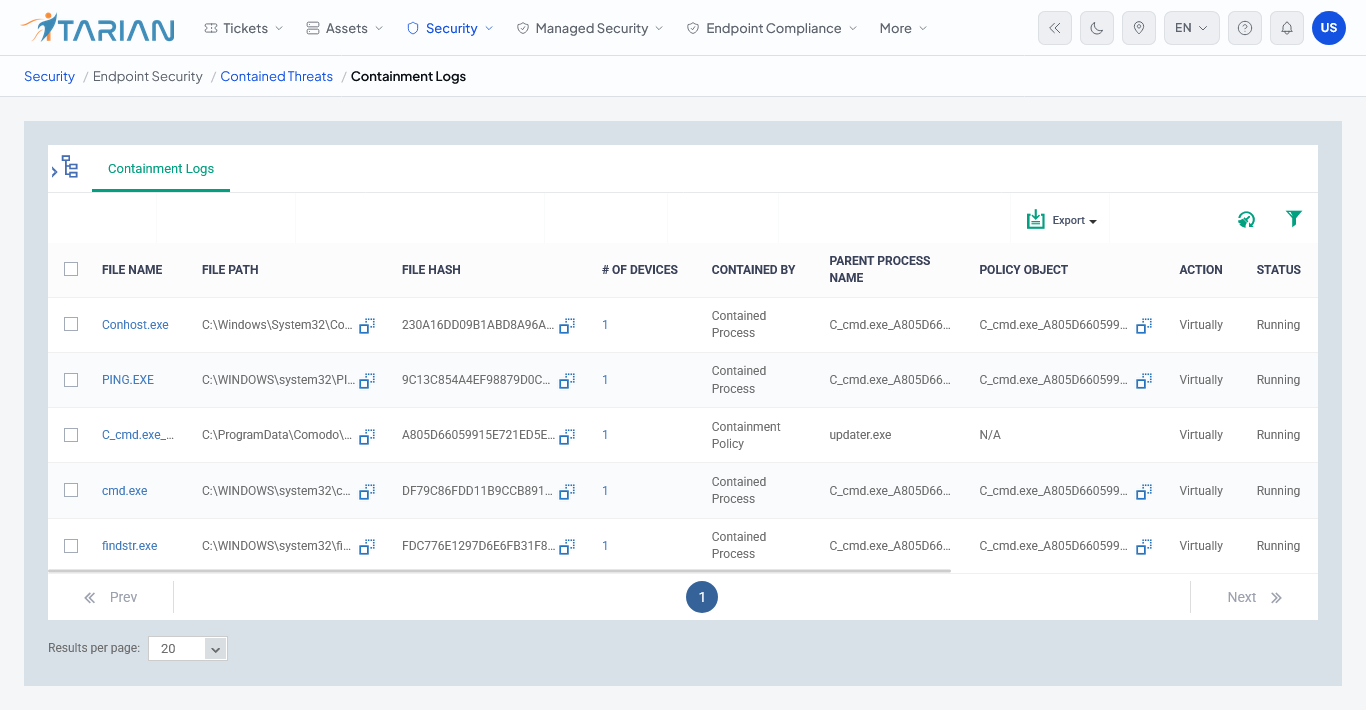
Automatically contain unknown executables so they can be analyzed without being allowed to compromise the endpoint.
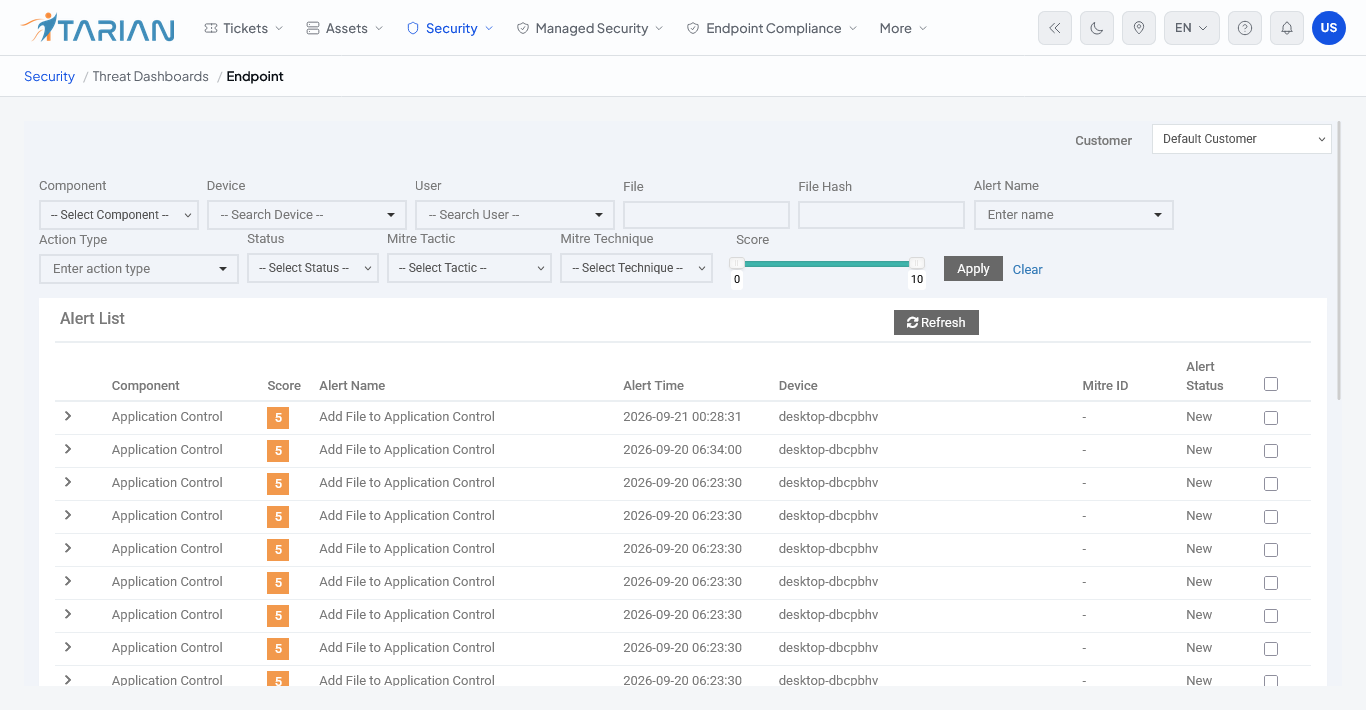
Continuously monitor endpoint activity and quickly identify suspicious behavior and threats as they emerge.
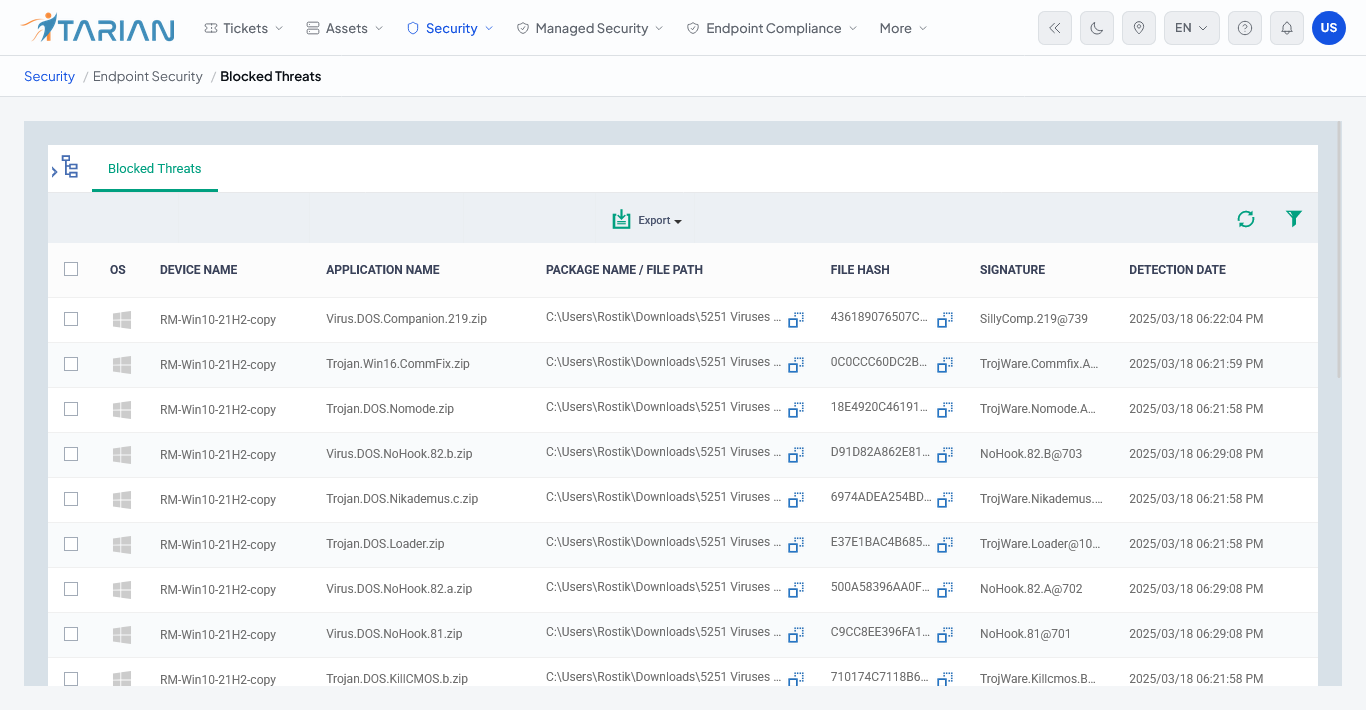
Protect endpoints against known and unknown malware using multiple layers of prevention and detection.
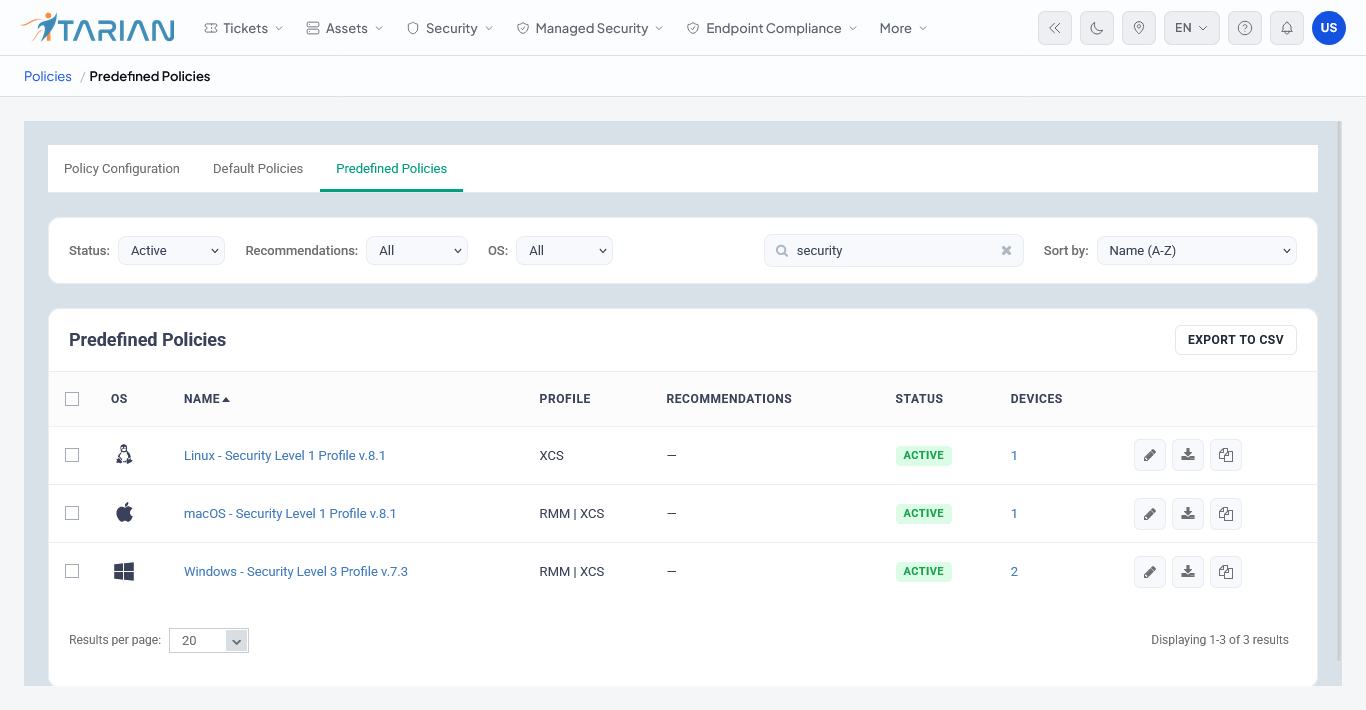
Investigate security events, apply security policies and take appropriate response actions from a centralized console.
Powered by Xcitium, ITarian Endpoint Security isolates unknown executables in a virtual environment during evaluation.
Stop unknown files from executing freely.
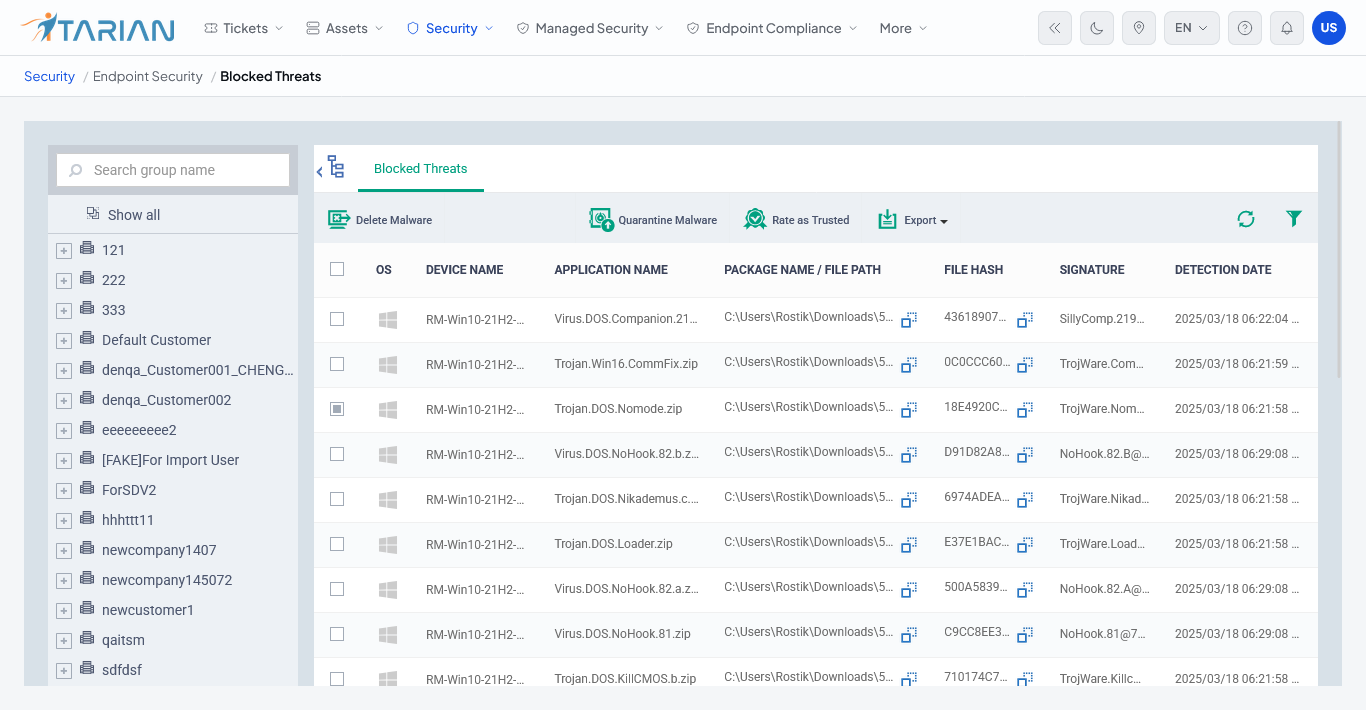
Identify known and suspicious threats in real time.
Isolate unknown or malicious activity before it can spread.
Manage incidents and act from one console.
ITarian brings endpoint security information into the broader operational context, so security events can be understood alongside the device, customer, ticket and related activity.
Suspicious activity is detected on a managed endpoint.
See the device, user, security status, and related activity.
Review the threat, severity and relevant context to determine the next steps.
Contain, remediate, investigate or escalate the security event.
Capture the action taken and outcome in the service workflow.
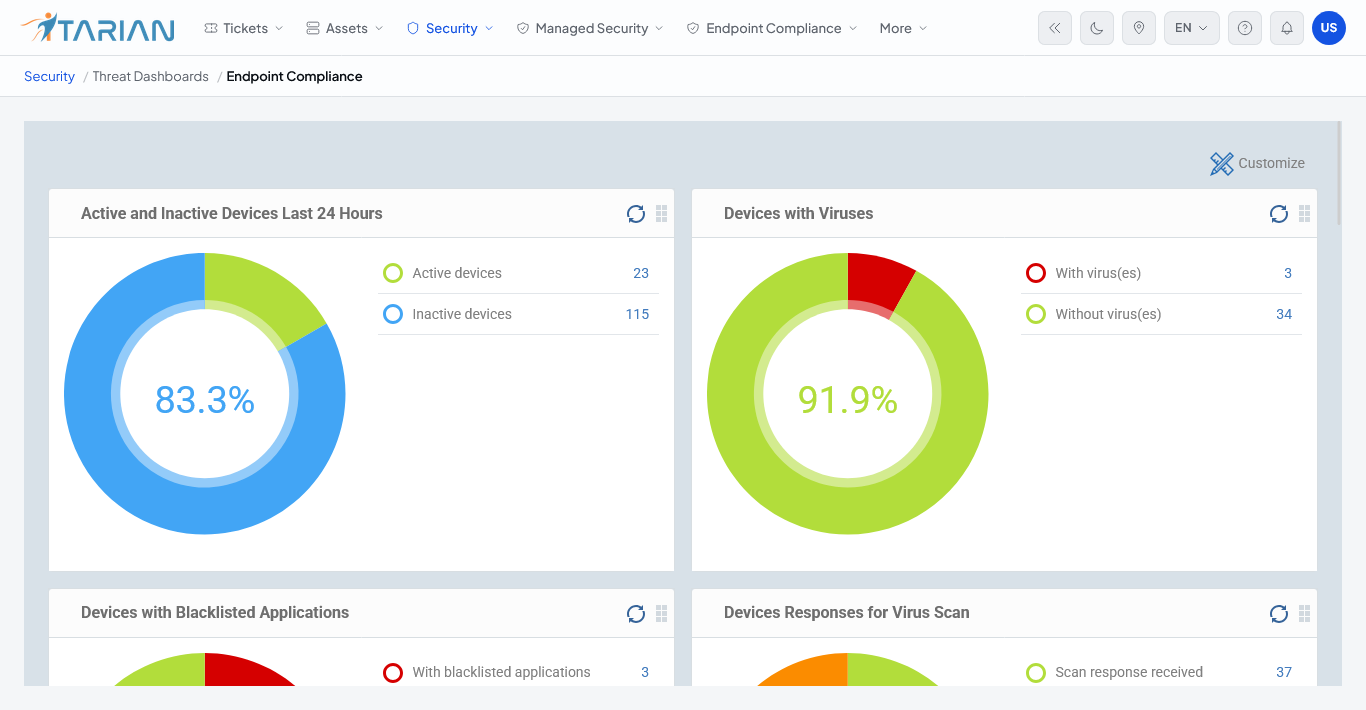
Track endpoint status, threats, containment and ransomware protection, with profiles, scan history and reporting.
Security Overview: Get a centralized view of endpoint protection, security status and activity across managed customer environments.

Endpoint Status: View the current security status, activity, and protection details for endpoints across managed customer environments.

Threats: Review detected threats, affected endpoints, and security details to understand what requires attention.

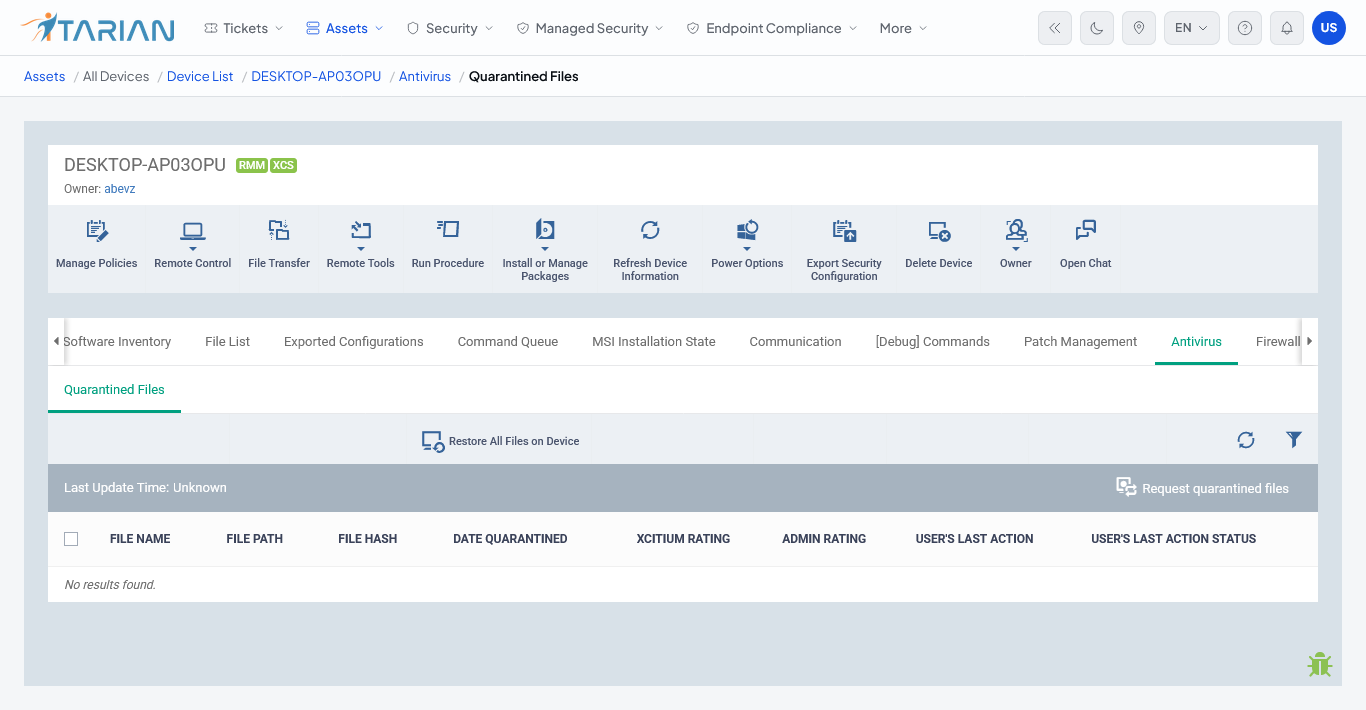
Containment: Apply available containment actions to affected endpoints when a security event requires immediate intervention.

Security Profiles: Manage security profiles and protection settings to apply consistent endpoint security controls across environments.

Ransomware Protection: Monitor ransomware protection status and activity across managed endpoints to identify potential security concerns.

Scan History: Review completed security scans, detection results, and endpoint activity to understand previous security events.

Reporting: Review endpoint security activity and protection data through centralized reports across managed environments.

One AI-native platform to run and grow your MSP.